
Hackers Hijack Hotel Wi-Fi to Steal Microsoft 365 Credentials via Fake Login Pages
APTcyber_warfareintelligencesecuritycyberespionagehackinghacking_newshotel_Wi-Fiinformation_securityIT_information_securityWi-Fi_hijackingcredential_theftMicrosoft_365network_security
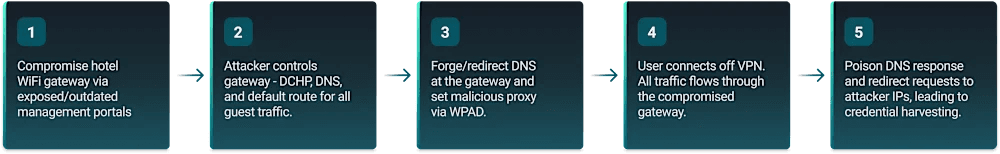
Hackers compromised hotel Wi-Fi gateways to redirect users to fake Microsoft 365 login pages and steal credentials. ReliaQuest’s threat research team documented attackers hijacking Wi-Fi gateways at hotels and conference centers, enabling automatic redirection of guests to malicious login portals without requiring phishing emails or malicious attachments. The attack method relies on manipulating network traffic to intercept authentication attempts. No specific threat actor, dates, or technical indicators (e.g., CVE IDs) were disclosed in the report. The primary impact involves unauthorized access to corporate or personal Microsoft 365 accounts via stolen credentials.