
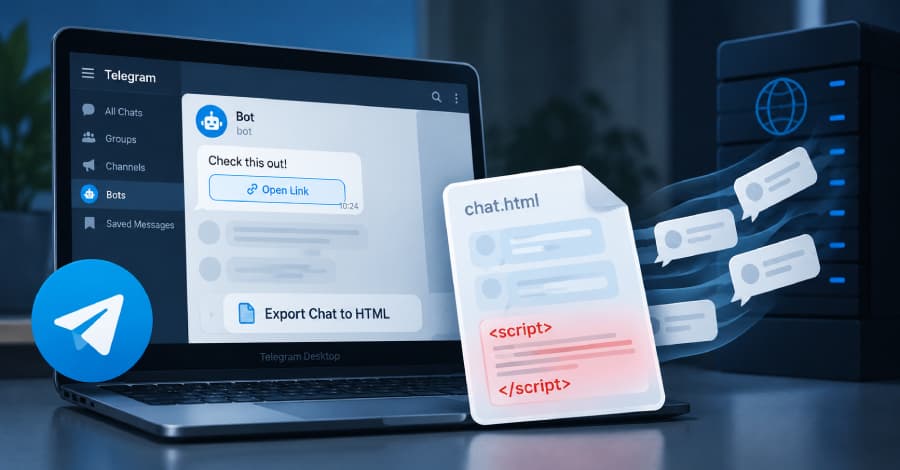
Telegram Desktop Flaw Allowed Hidden JavaScript Execution in Exported Chat Files
CybersecurityVulnerabilitiesMessaging AppsJavaScript Exploits
A flaw in Telegram Desktop allowed a bot's message to plant hidden JavaScript inside chats that executed when users exported conversations to HTML files and opened them in a web browser. Security researchers at ExPatch disclosed the vulnerability in a writeup published on September 12. In Telegram, the malicious message appeared ordinary with a link button, but the embedded script could copy every message in the exported file once opened in a browser. The JavaScript remained hidden within the chat export and only activated upon opening the HTML file.