
PEERSTITCH Malware Compromises 500+ Firewalls Through FortiManager Exploit
Breaking NewsHackingMalwareSecurityCVE-2024-47575CVE-2025-61624FortiManagerPEERSTITCHFirewallTelecomIntrusionCyber Attack
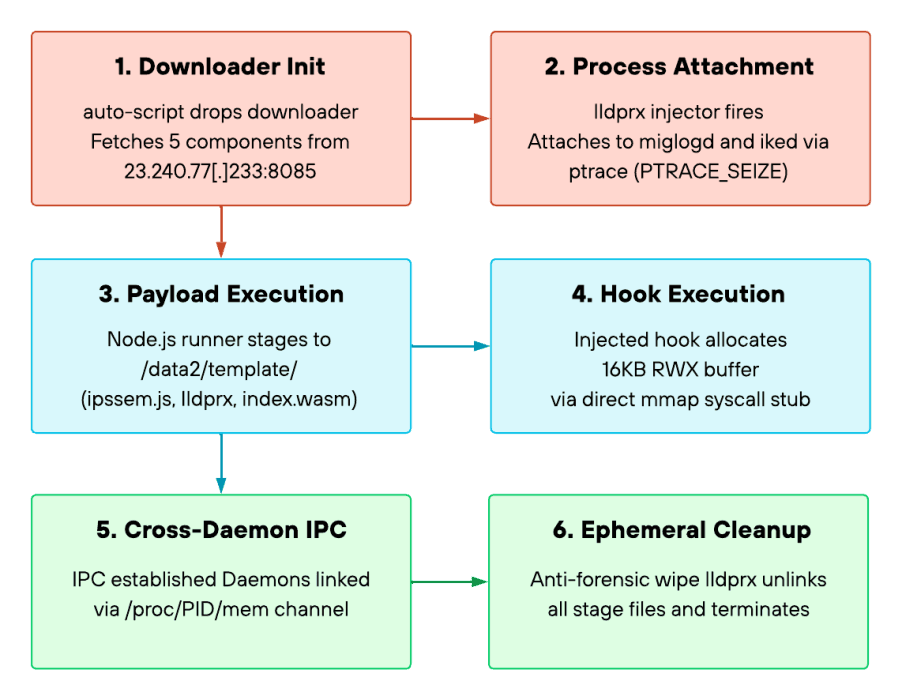
PEERSTITCH malware was deployed as a stealthy implant during an intrusion that began in September 2024, targeting a telecom managed service provider through a compromised FortiManager appliance. The malware exposed over 500 firewalls and evaded detection by operating inside FortiOS memory to maintain persistent access. Palo Alto Networks Unit 42 documented the operation. The article references CVE-2024-47575 and CVE-2025-61624 in the metadata tags.